Preview. DealReady is not open to customers yet. For early access, write to info@dealready.dev.
DealReady
For B2B SaaS · built for the first enterprise deal

Pass the security review.
Close the deal.

Your buyer sent a security questionnaire. Within a week you get it answered with sources, a report on your code and perimeter mapped to SOC 2 and ISO 27001, and fix guidance.

No credit card for the free scan · read-only GitHub access · EU hosting
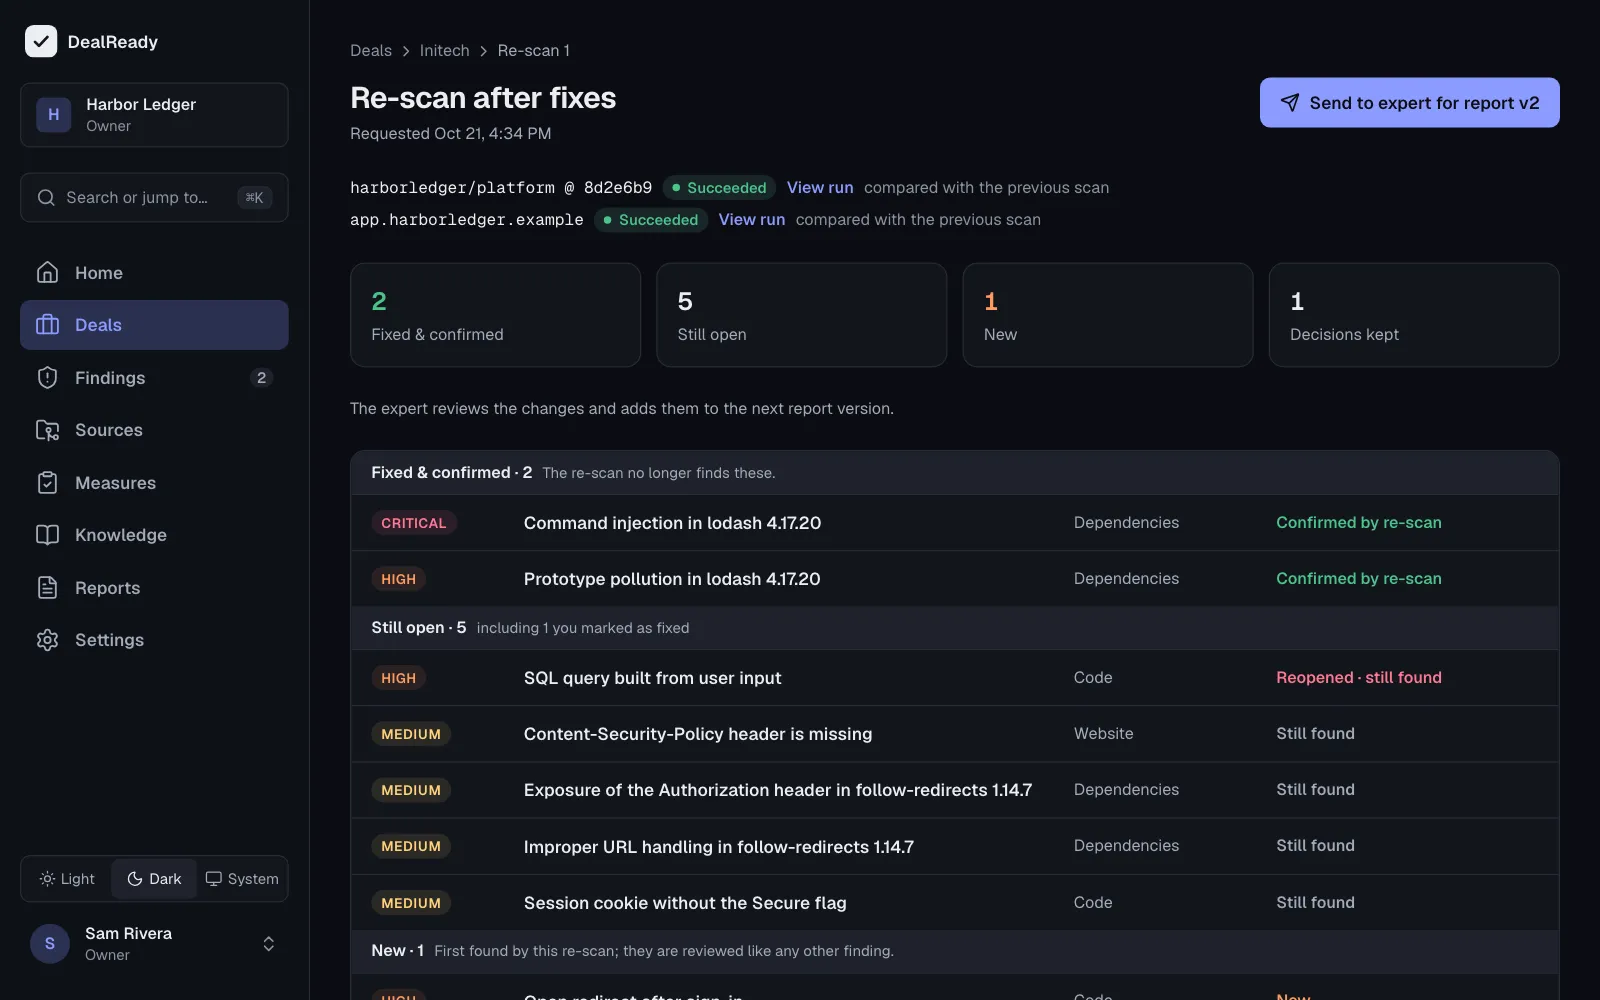
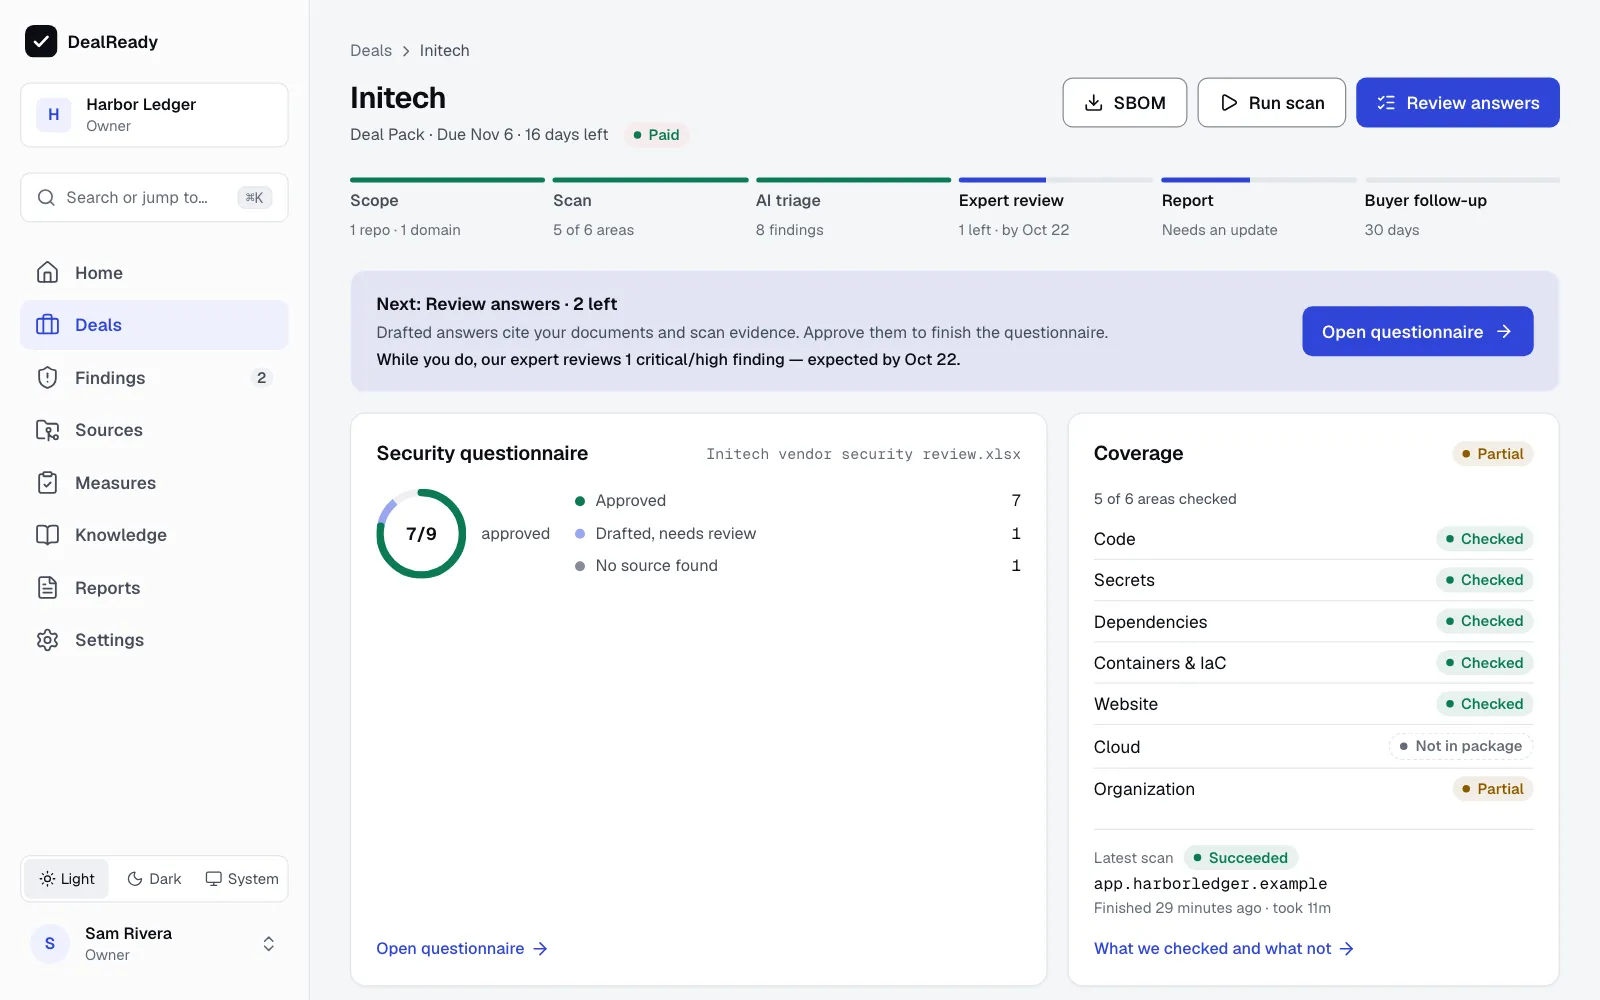
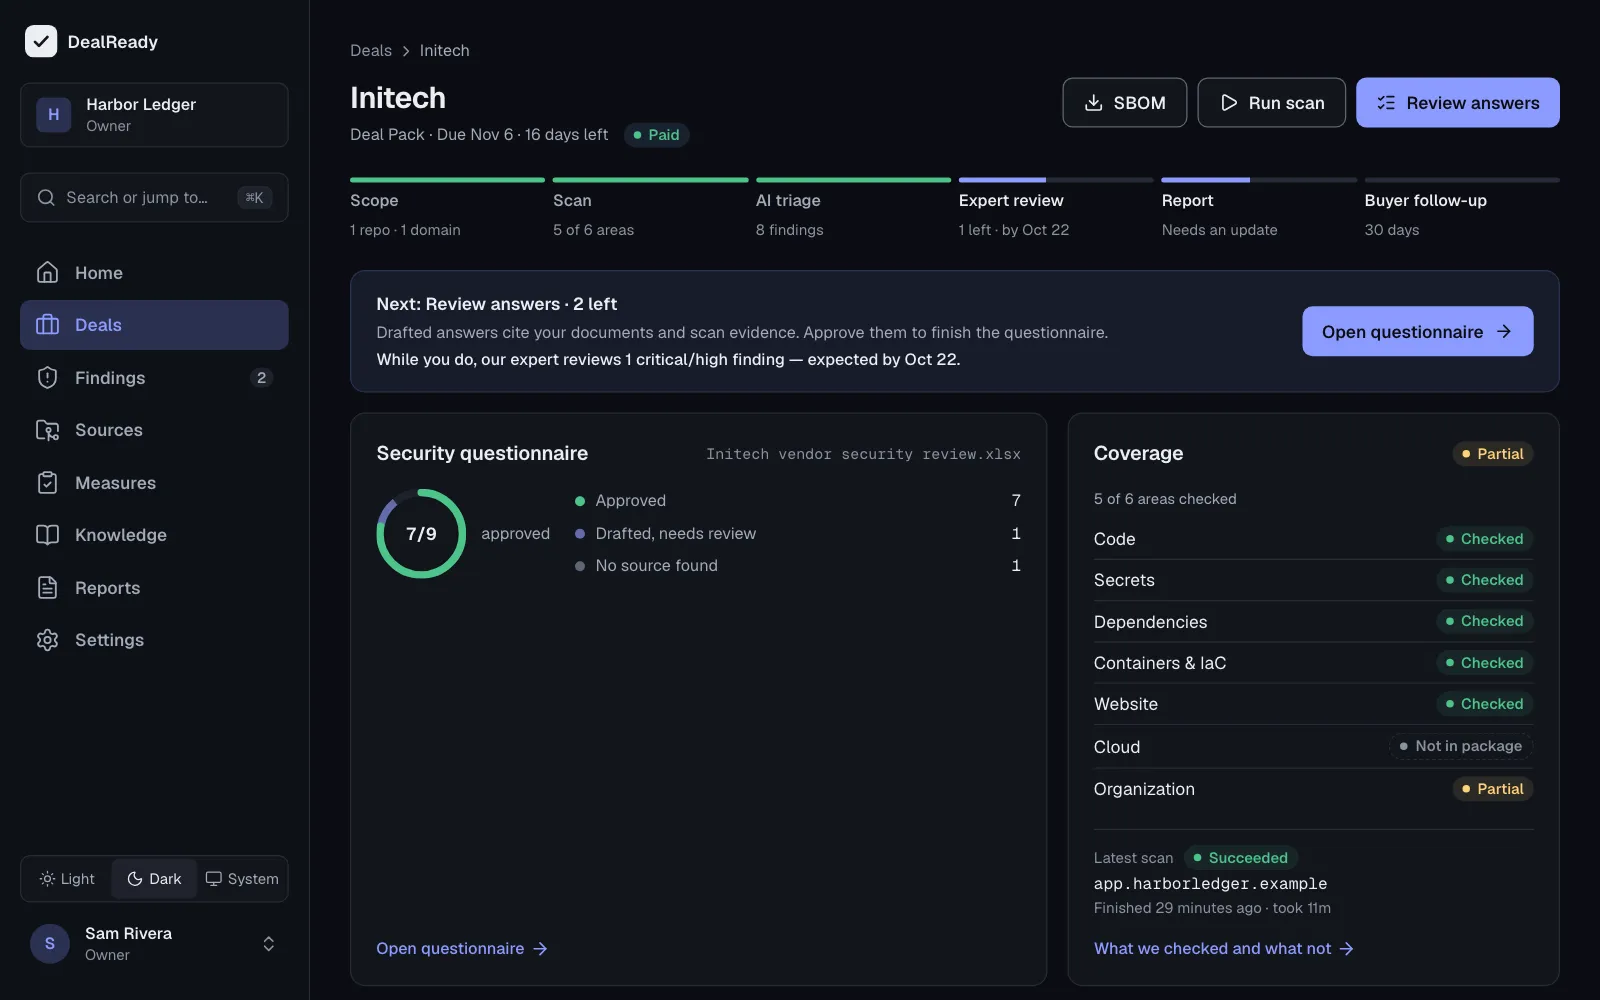
A deal in DealReady: progress from scope to buyer follow-up, the questionnaire, coverage by area, findings and the report status
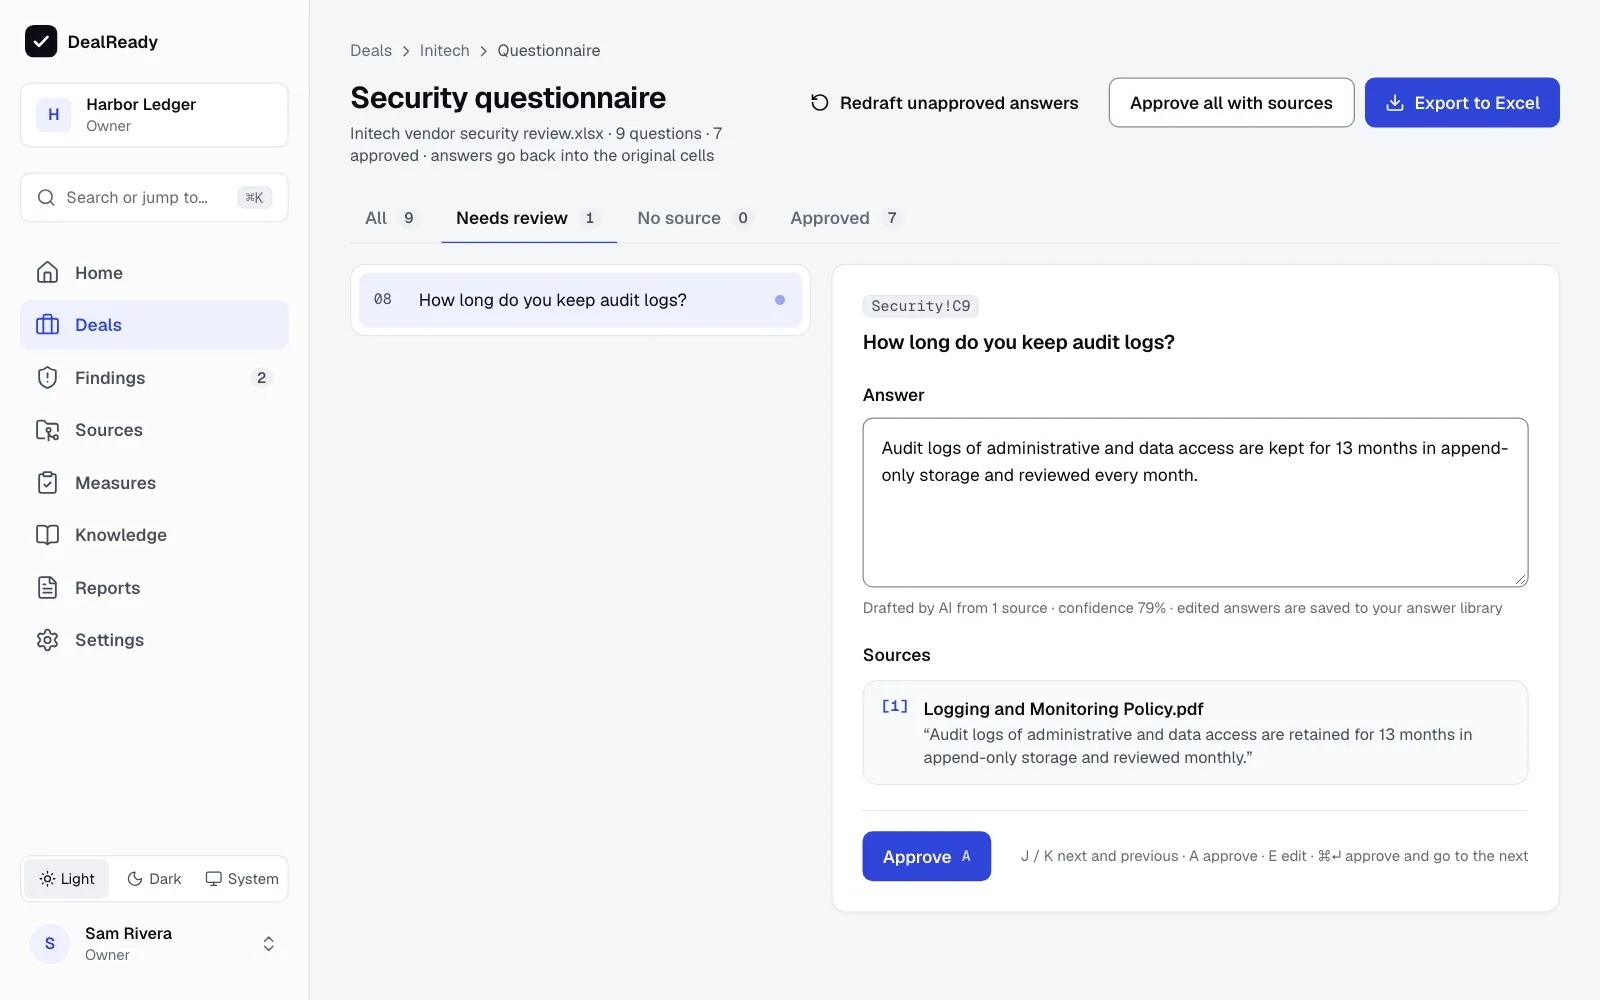
  • Questionnaire answeredEvery answer cites a policy or a scan result
  • Code and perimeter checkedCode, secrets, dependencies, containers, website
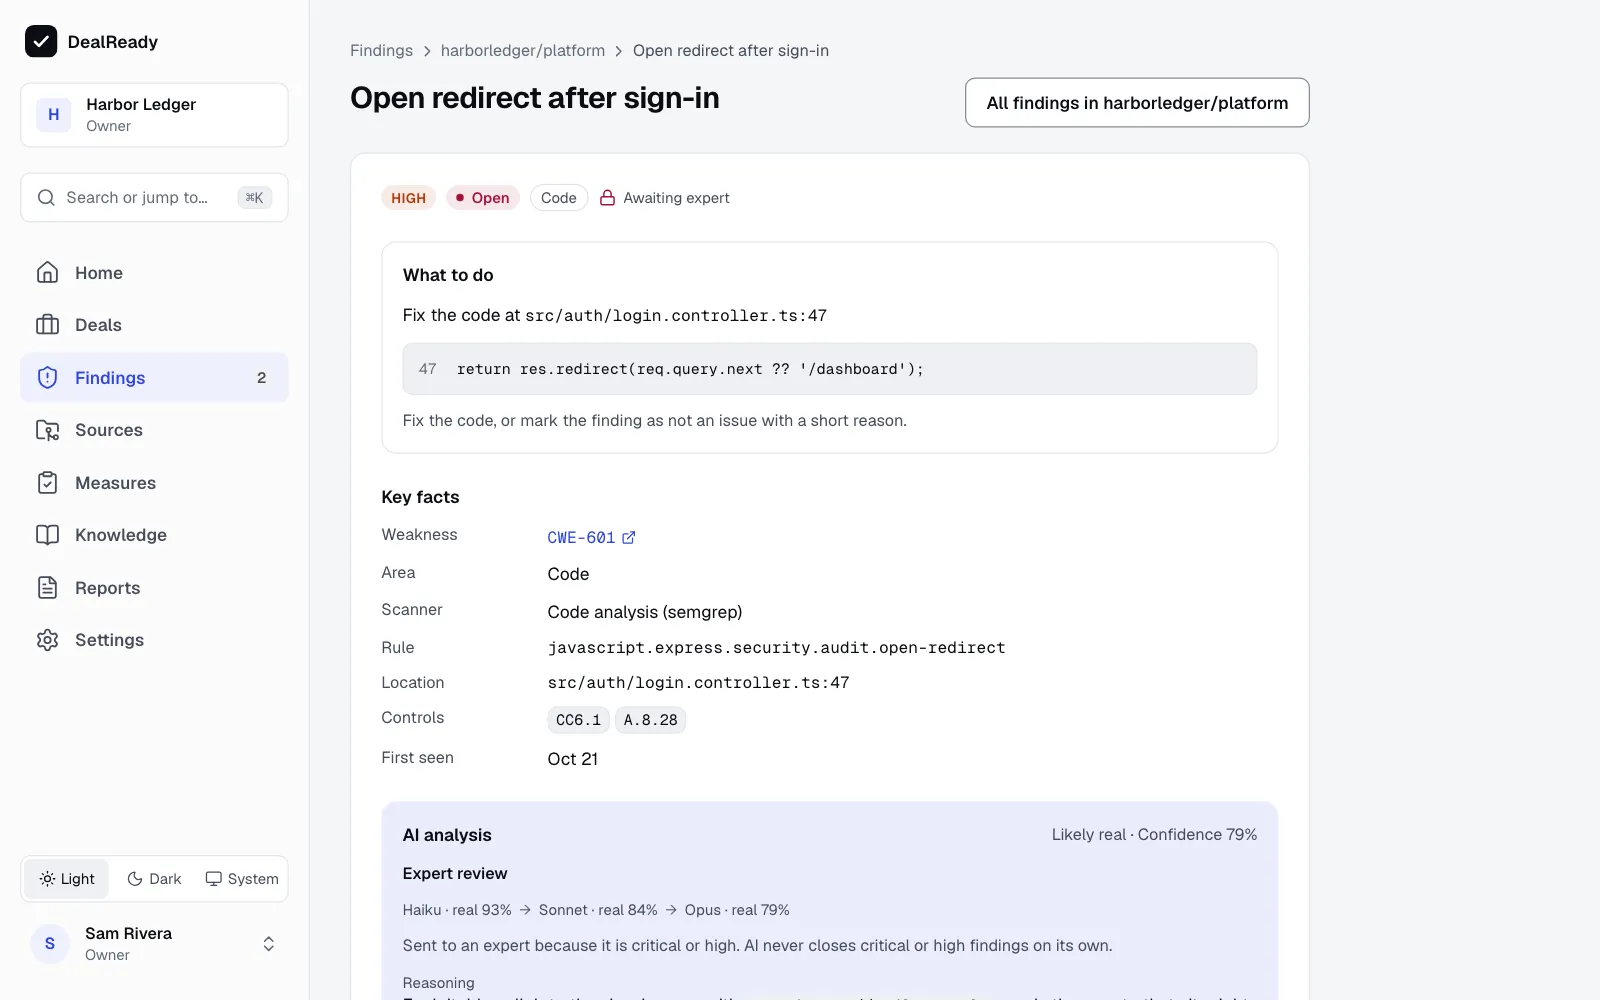
  • Findings confirmed by an expertAI filters the noise, a person signs off
  • A report the buyer acceptsPDF mapped to SOC 2 and ISO 27001
HOW IT WORKS

From the buyer's questionnaire to a signed deal — every step, as you will see it

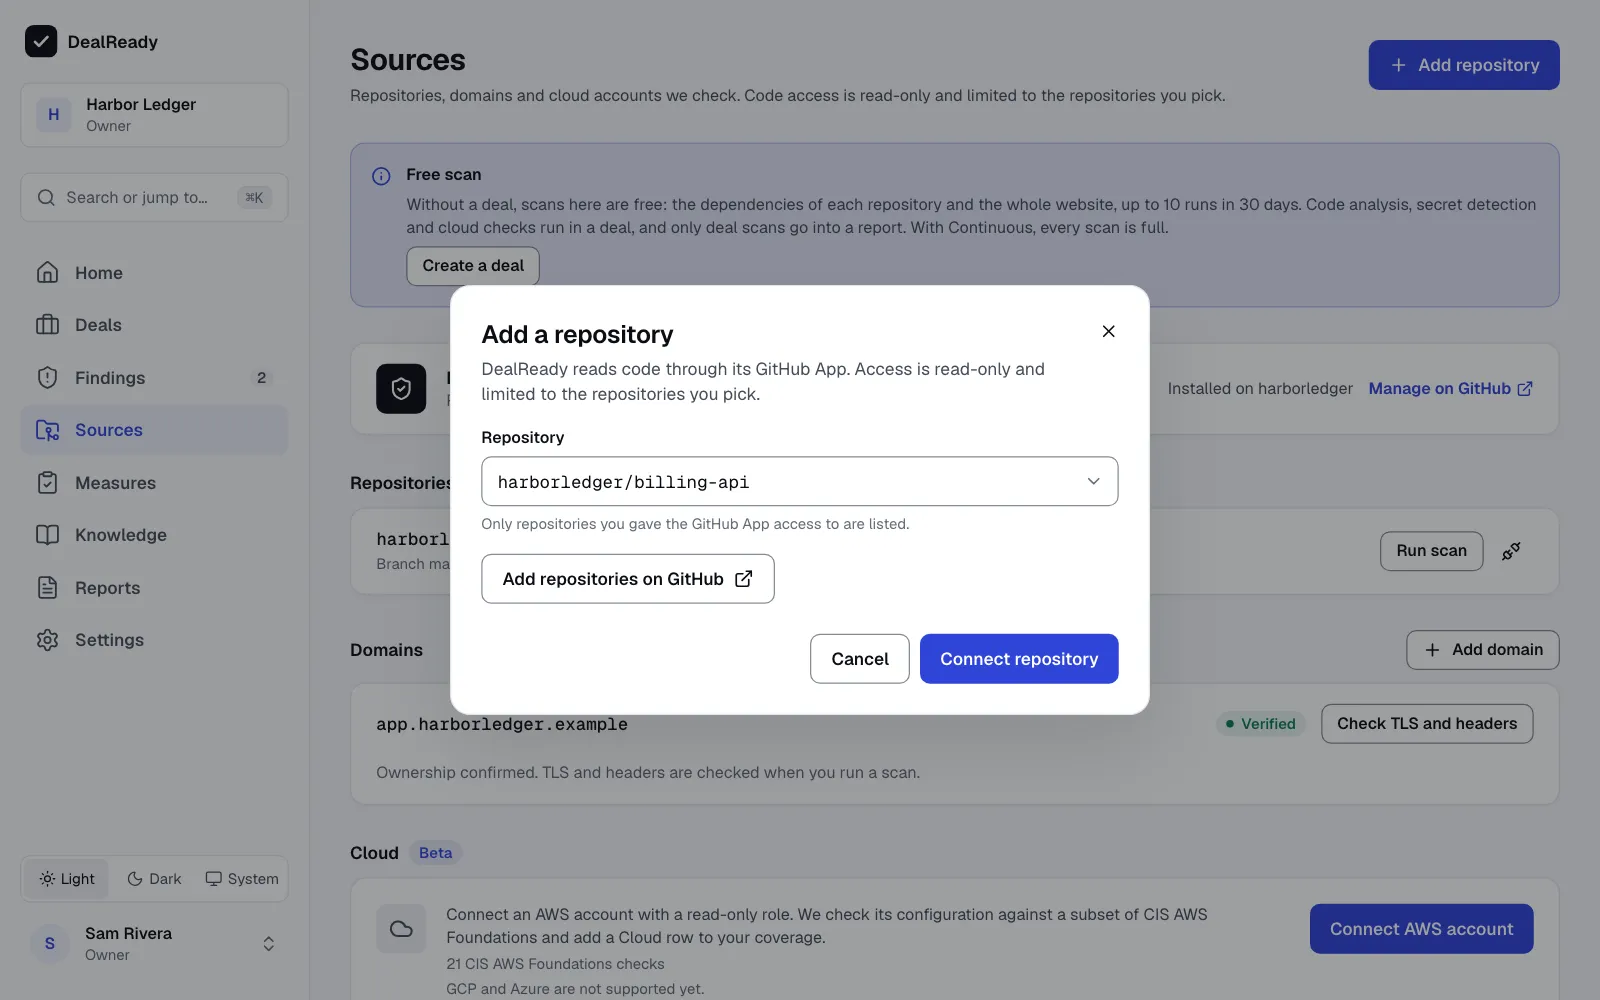
Sources: connecting GitHub repositories and a domain
1 / 7

Connect your code and domain

Install the read-only GitHub App on the repositories you pick and verify your domain with one DNS record. Nothing else gets access.

In: Free scan, Quick Check, Deal Pack, Continuous, Pre-pentest
PACKAGES

Which steps each package covers

The same seven steps, side by side. Full comparison with every limit on the pricing page

StepFree scan
€0
Quick Check
€490
Deal Pack
€1,900
Continuous
€3,480/yr
Pre-pentest
€490
Connect your code and domainYour repositories and a domain, no card neededRepositories and domains of the dealRepositories and domains of the dealEvery repository, every pushRepositories and domains of the deal
We scan code, secrets, dependencies, containers and the websiteDependencies and websiteCode, secrets, dependencies, containers & IaC and websiteAll 5 areas, plus your organizational measuresAll 5 areas, plus your organizational measuresCode, secrets, dependencies, containers & IaC and website
AI sorts real issues from noiseAI triage of every findingAI triage of every findingAI triage of every findingAI triage on every pushAI triage of every finding
An expert confirms what matters—Critical and high findingsExpert validation and fix guidanceExpert validationExpert validation
The buyer's questionnaire, answered with sources——One questionnaire, up to 300 questionsUp to 4 a year, from your answer library—
A report the buyer accepts—Short report: findings and fix guidancePDF, valid for 90 daysUpdated every monthFindings handed to the pentest partner
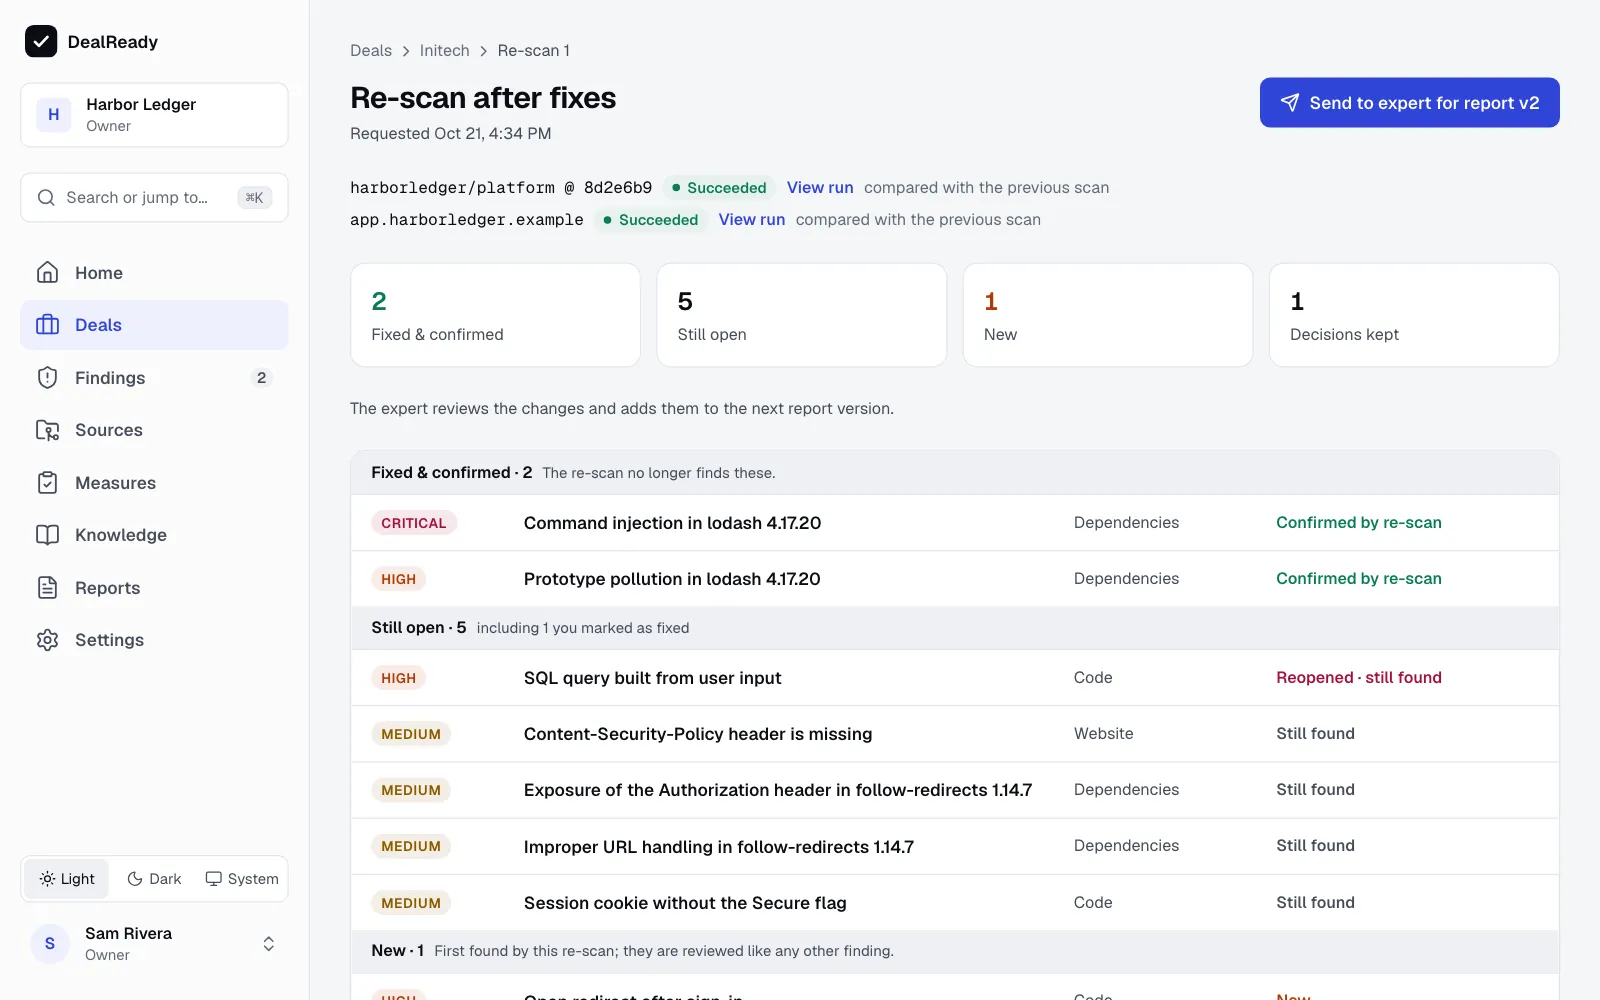
You fix, we confirm with a re-scan—One re-scanOne re-scan, buyer follow-ups for 30 daysScan on every pushIntroduction to a certified partner (fee separate)
THE REPORT

What the buyer's security team reads

  1. Scope stated plainly. Each area checked, checked in part or not checked — and what is outside the review.
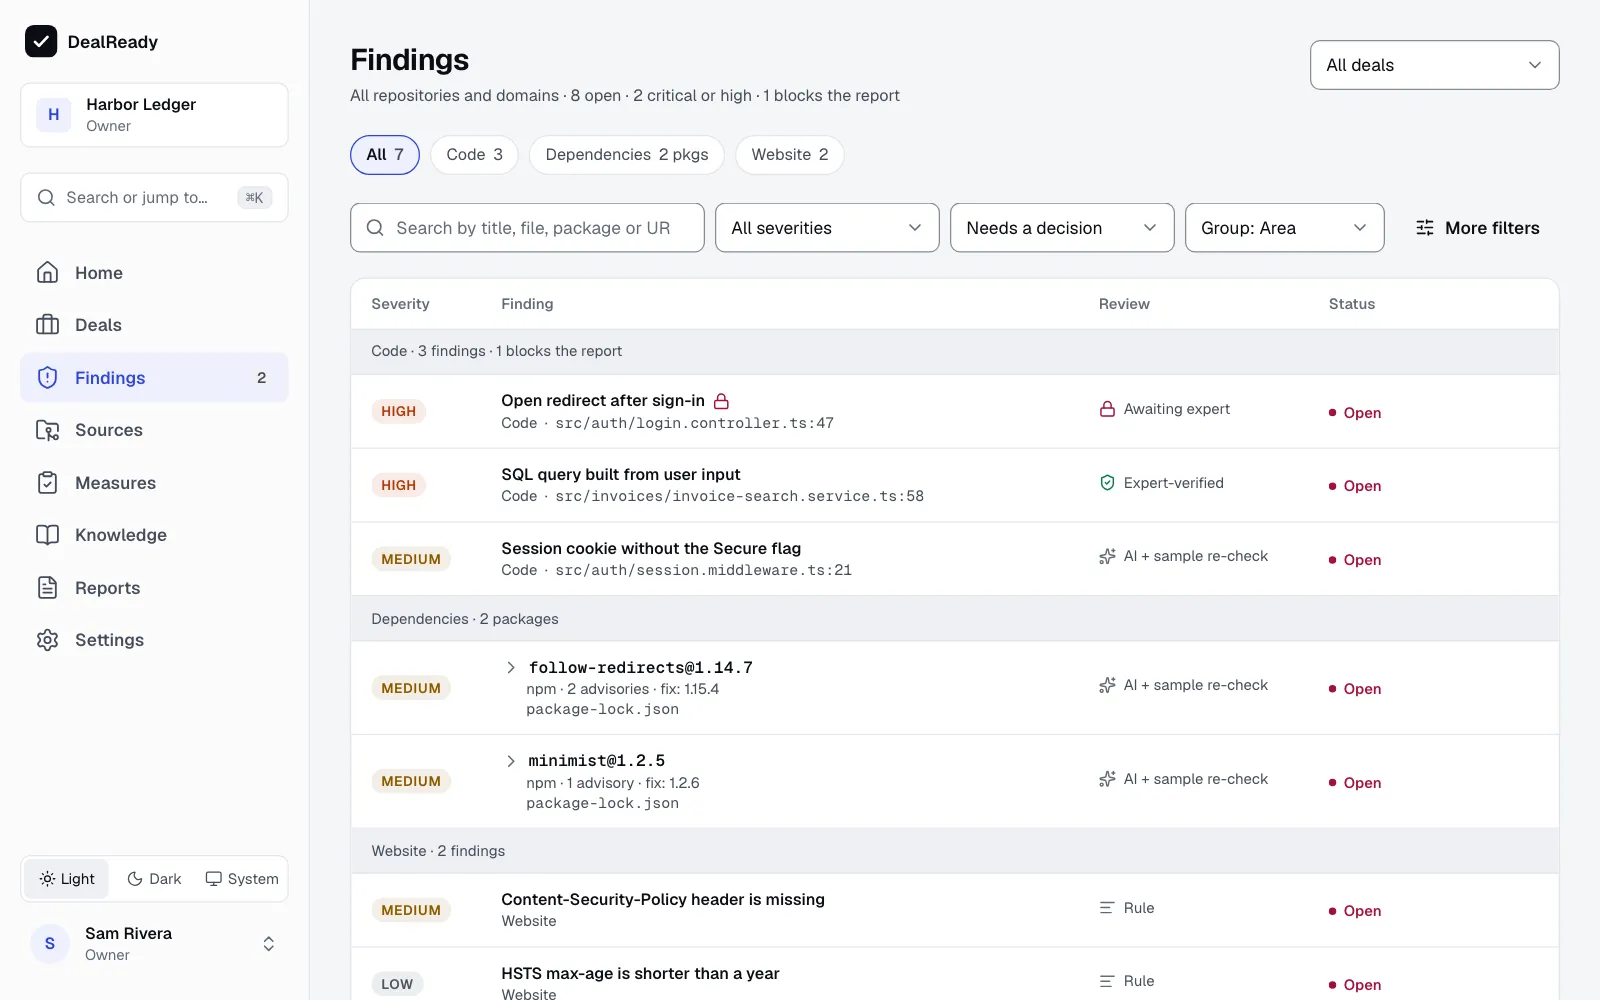
  2. Issues, not noise. One advisory in three lockfiles counts once; packages show the version that fixes them.
  3. Who stands behind each finding. Expert-verified, a deterministic check, or AI with an expert re-checking a sample.
  4. Mapped to SOC 2 and ISO 27001. Controls per finding, valid for 90 days in a Deal Pack.
Download a sample report (PDF)
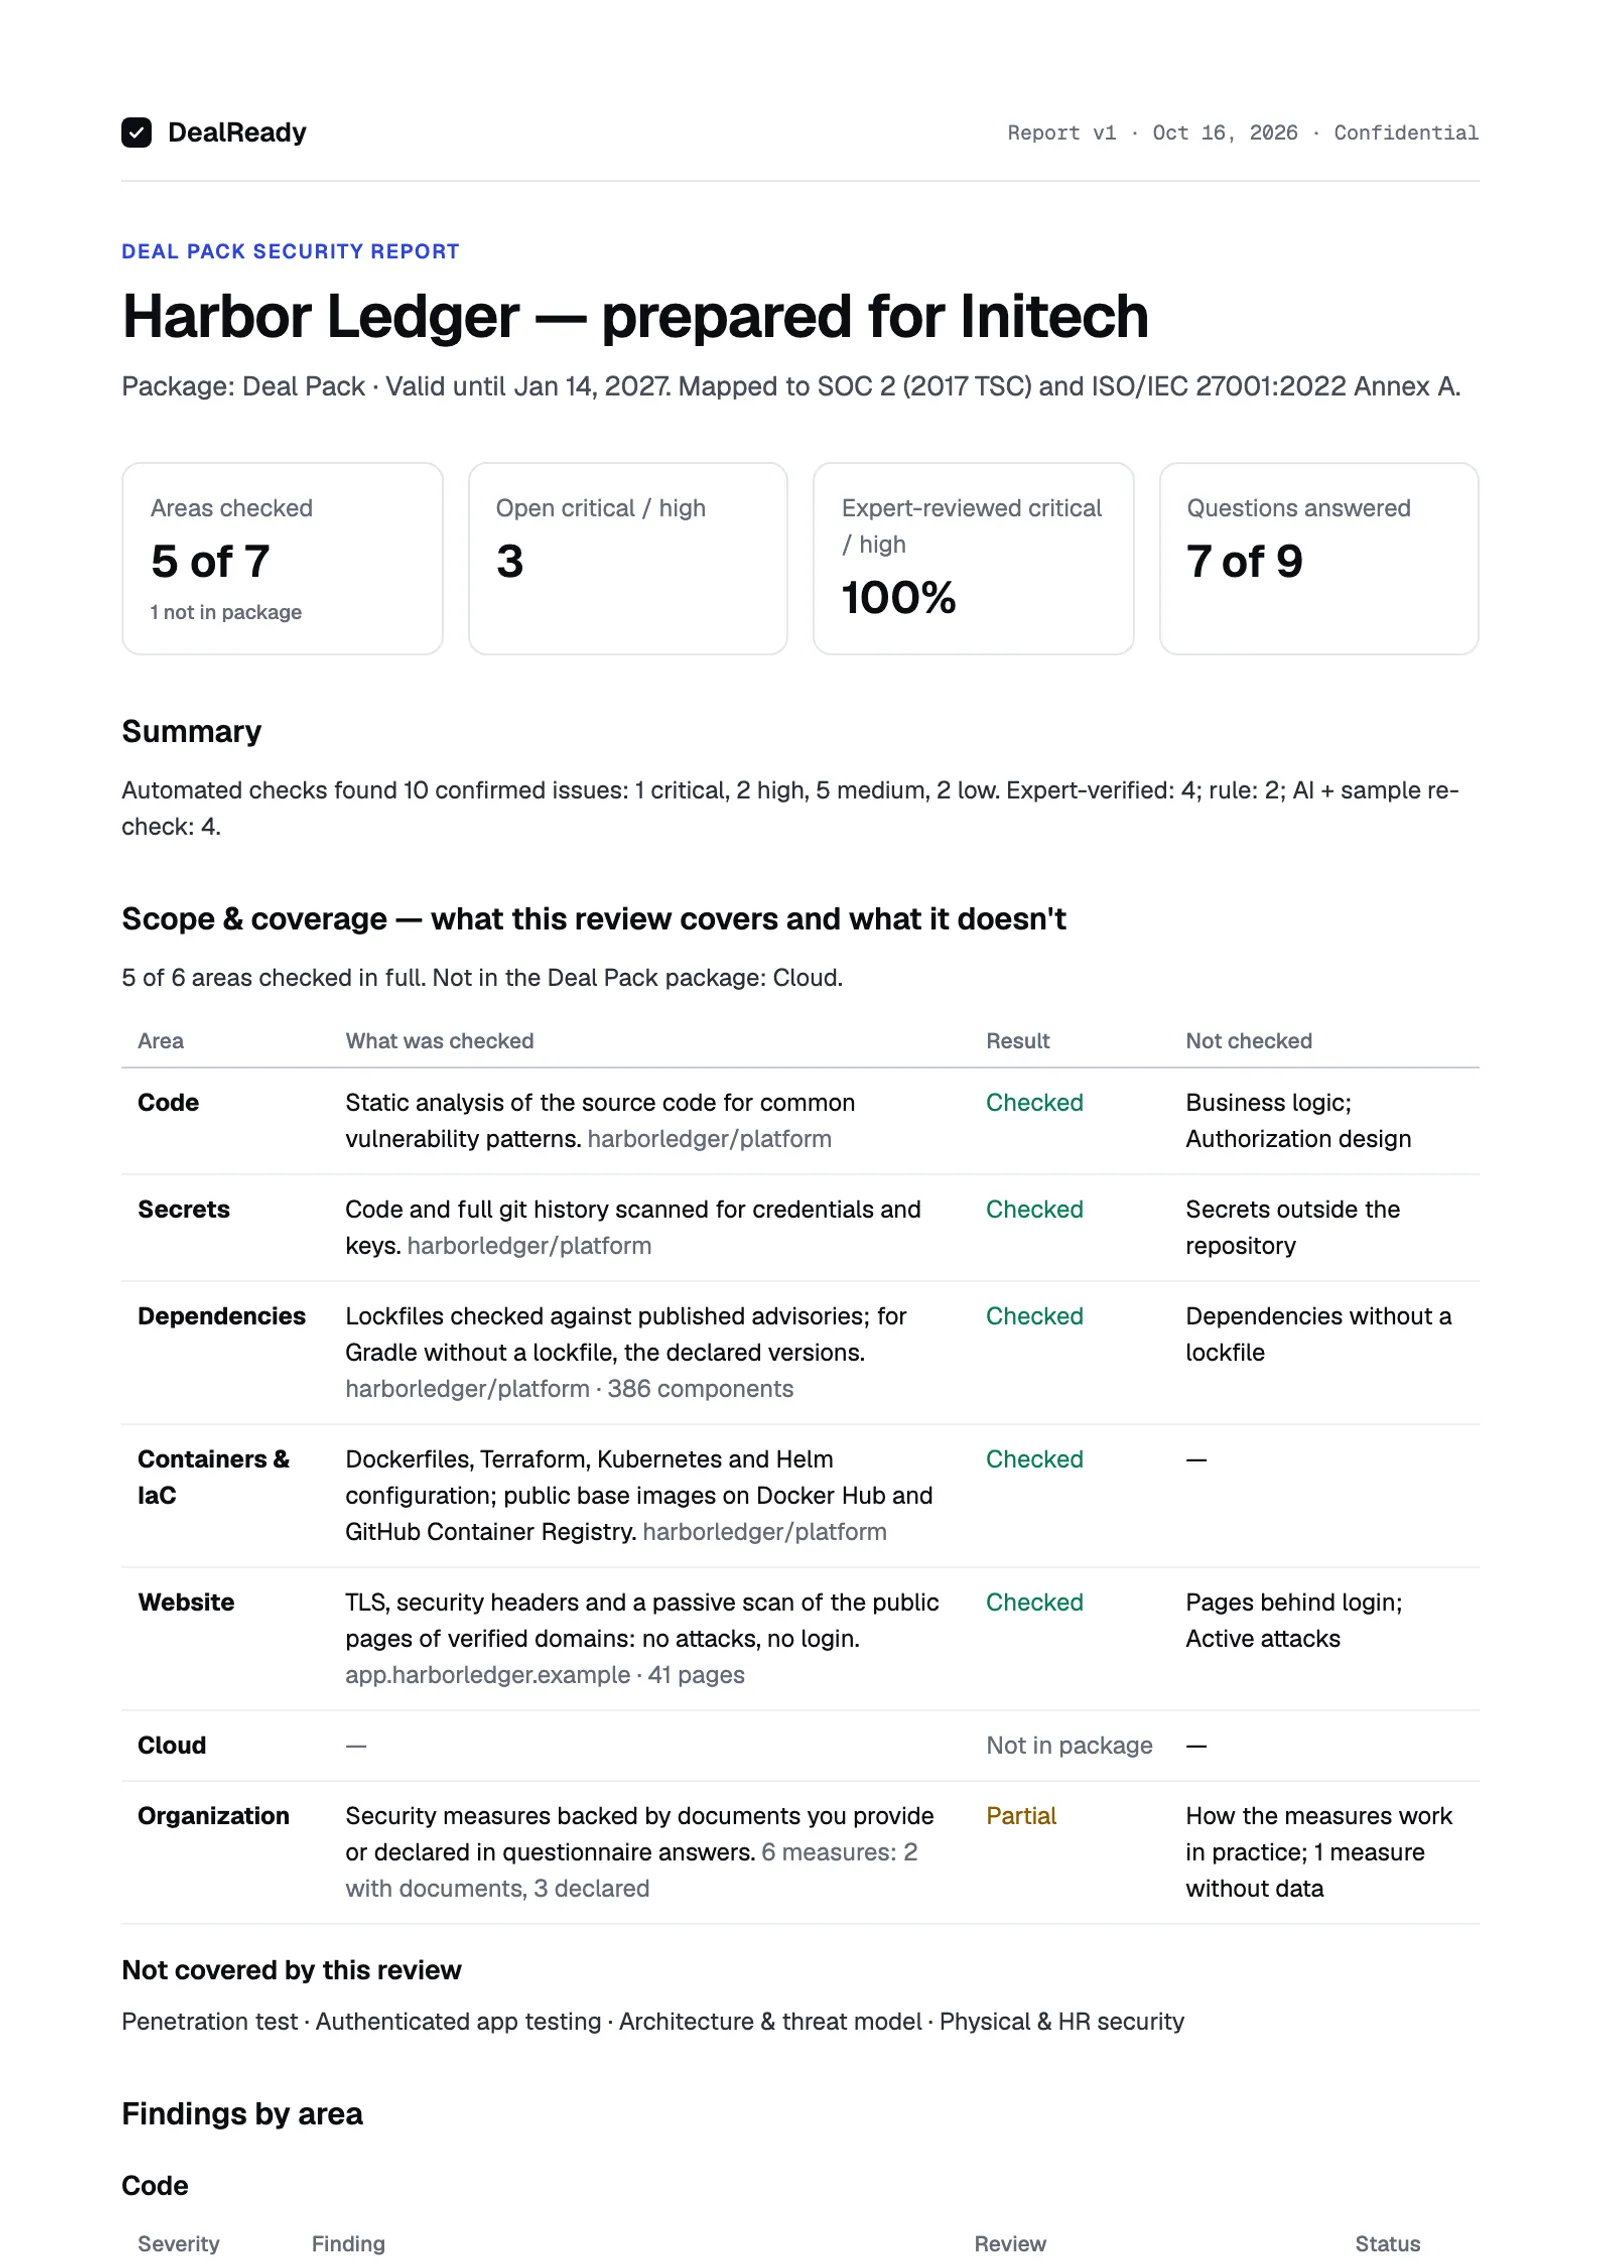
First page of a Deal Pack report: areas checked, open critical and high, expert-reviewed share, questions answered, and the scope table
COVERAGE

What a review covers — and what it doesn't

Every report shows the same table: each area checked, checked in part or not checked, and what is outside the review. Nothing is implied beyond it.

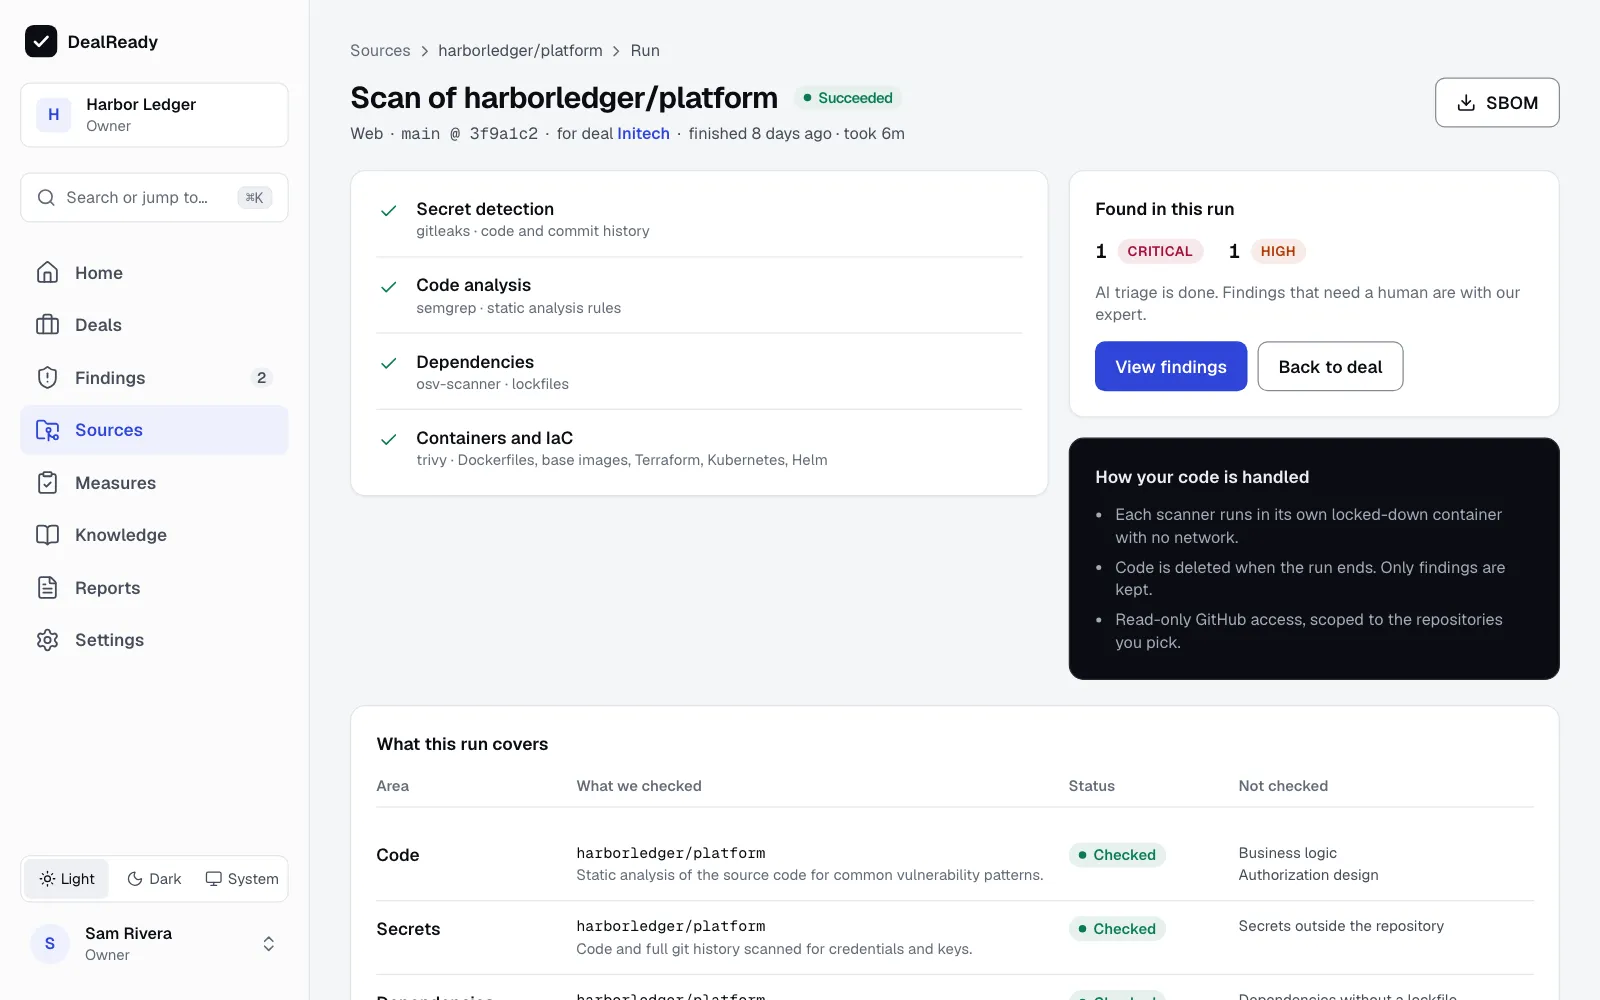
  • CodeStatic analysis of the source code for common vulnerability patterns.iOS and Android source code (beta): static analysis, the app binary is not tested.Not checked: Business logic, authorization design
  • SecretsCode and full git history scanned for credentials and keys.Not checked: Secrets outside the repository
  • DependenciesLockfiles checked against published advisories; for Gradle without a lockfile, the declared versions.Not checked: Dependencies without a lockfile
  • Containers & IaCDockerfiles, Terraform, Kubernetes and Helm configuration; public base images on Docker Hub and GitHub Container Registry.
  • WebsiteTLS, security headers and a passive scan of the public pages of verified domains: no attacks, no login.Not checked: Pages behind login, active attacks
  • OrganizationSecurity measures backed by documents you provide or declared in questionnaire answers.Not checked: How the measures work in practice

Not covered by any package

  • Penetration test
  • Authenticated app testing
  • Architecture & threat model
  • Physical & HR security

If your buyer needs one of these, the report states that it was not covered. Pre-pentest prepares you for the first one and introduces a certified partner.

SECURITY

We handle your code the way we'd want ours handled

  • Isolated scans. Every scanner runs in its own locked-down container with no network access.
  • Code is deleted after each run. We keep findings, not your repository.
  • Least privilege. Read-only GitHub App, scoped to the repositories you pick.
  • Passkeys and MFA for every account, with tenant isolation enforced in the database.
PRICING

One deal, or every deal this year?

A Deal Pack is a fixed price for the deal on your desk. Continuous is a yearly plan that pays off from the second questionnaire.

How many security questionnaires do you expect this year?
1 Deal PackCheaper this year€1,900One questionnaire, a report valid 90 days, re-scan and follow-ups
Continuous, billed annually€3,480Up to 4 questionnaires; you would use one

Take the Deal Pack. For a single deal the yearly plan costs more; it pays off from the second questionnaire.

  • Free scanCurious where you stand€0No card needed
    • Dependencies and website
    • AI triage
    Start free
  • Quick CheckBefore the buyer asks€490One-off
    • Full scan of five areas
    • Expert review of critical and high
    • Short report: findings and fix guidance
    • One re-scan after your fixes
    Choose
  • Deal PackOne dealOne deal on your desk now€1,900One-off, per deal
    • One questionnaire, up to 300 questions
    • Expert-validated findings and fix guidance
    • Full report for the buyer, valid 90 days
    • Re-scan and 30 days of follow-ups
    Start a Deal Pack
  • ContinuousSelling to enterprises all year€3,480 a year€290 a month billed annually
    • Up to 4 questionnaires a year
    • Scan on every push
    • Report updated monthly
    • Pays off from the second questionnaire
    Choose

Add-ons

  • Rush delivery, under 5 business days+50%
  • Extra questionnaire€290
  • Extra repository€190

Prices exclude VAT: EU business customers are billed under the reverse charge.

Need a pentest? Pre-pentest (€490) gets you ready for it, and we introduce a certified partner. The partner's fee is separate.

Compare every package and limit

Questions

Is this a pentest?

No. It's automated scanning with expert validation that prepares you for the questionnaire — and for a pentest if the buyer requires one. We'll introduce a certified partner.

Does it give us SOC 2 or ISO 27001?

No certification is issued. The report maps your evidence to those controls, which is what buyers usually ask to see first.

Which stacks do you support?

Any repository for secrets and dependencies; deep checks for Next.js and NestJS, and iOS and Android source code (beta). We read the source; the app binary is not tested and the app is not run. More frameworks next.

Who sees our code?

Scanners in an isolated container, and the model only sees the snippet around a finding. Code is deleted after the run.

Got a questionnaire on your desk? Start it today.

Upload your questionnaire